Polarsteps photos and locations exposed: journalists accessed data of 23 million users
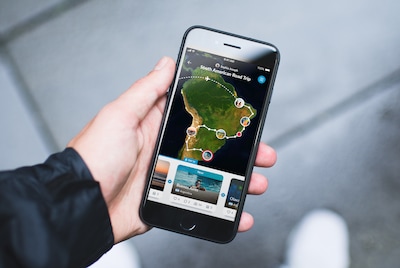
The Amsterdam-based travel app Polarsteps suffered a data breach exposing the personal information and GPS locations of 23 million users. Cybersecurity researchers and the platform Follow the Money uncovered the vulnerability, which allowed unauthorized access to private user data, leading the company to report the incident to the Dutch Data Protection Authority.
The Amsterdam-based travel application Polarsteps recently experienced a significant data breach, exposing the personal information of approximately 23 million users. Security researcher Louis Couderc discovered that the app allowed unauthorized access to sensitive details, including private photos and precise GPS locations, even for content restricted to followers. The vulnerability was identified during the autumn of 2025, but reports suggest the company may have been aware of the issue for at least six months prior to its public exposure by the investigative platform Follow the Money.
Following the investigation, it was confirmed that millions of international user records could be downloaded due to the security oversight. In response to the breach, Polarsteps has officially notified the Dutch Data Protection Authority and implemented additional security measures to protect its user base. The company is currently working to resolve the vulnerabilities that allowed this widespread compromise of user privacy, as the platform faces scrutiny over its handling of sensitive travel data.
Based on reporting by ad. Translated and condensed by LocalHeadlines.